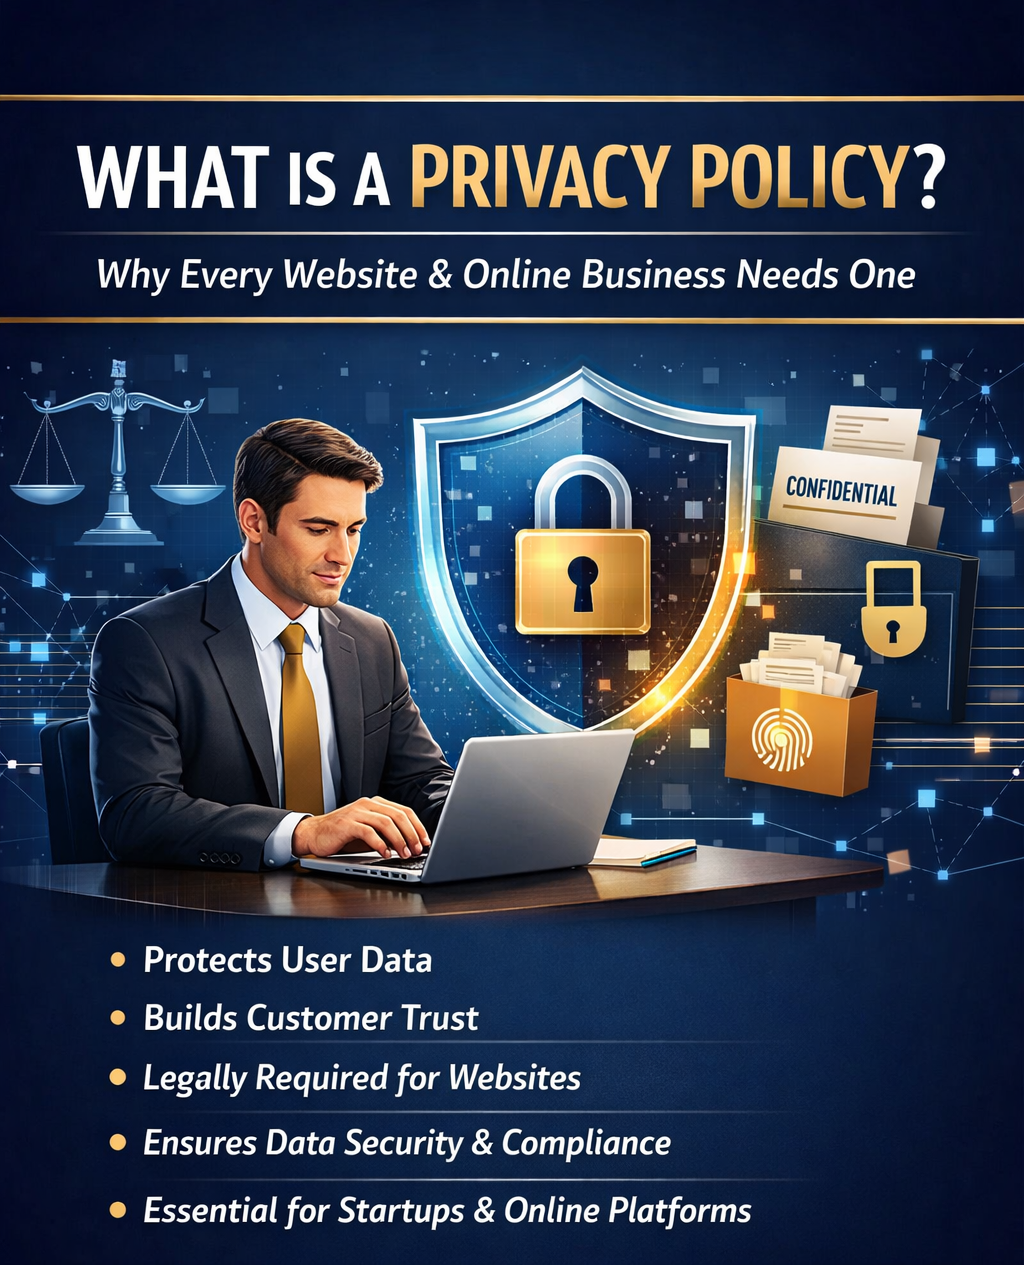
A Privacy
Policy is one of the most important legal documents for any website, mobile
application, online platform, or digital business operating in today’s
technology-driven world. As businesses increasingly rely on customer data to
provide services, users have become more conscious and concerned about how
their personal information is being collected, used, stored, and shared.
Whether someone is shopping online, consulting a lawyer through a legal-tech
platform, using a banking application, or simply filling out a contact form on
a website, some form of personal information is usually shared with the service
provider. In such a situation, a Privacy Policy acts as a bridge of trust
between the business and the user by clearly explaining how user information
will be handled.
In simple
words, a Privacy Policy is a legal statement or document that explains what
kind of information a company collects from its users, why that information is
collected, how it is used, whether it is shared with third parties, and what
measures are taken to protect that information. It also informs users about
their rights regarding their personal data. A properly drafted Privacy Policy
ensures transparency and helps users make informed decisions before using a
platform or service. It also demonstrates that the company respects the privacy
and confidentiality of its users.
The
importance of a Privacy Policy has increased significantly with the growth of
online businesses and digital services. Today, users share sensitive
information such as phone numbers, email addresses, payment details, addresses,
identity documents, and confidential communications on various platforms. If
such information is misused, leaked, or handled carelessly, it may cause
financial loss, identity theft, reputational damage, or breach of
confidentiality. Therefore, governments around the world have introduced data
protection laws requiring businesses to disclose their data handling practices
through Privacy Policies. In India, laws such as the Information Technology
Act, 2000, Information Technology Rules, and the Digital Personal Data
Protection Act, 2023 encourage and regulate the responsible collection and
processing of personal data. International laws such as GDPR in Europe and CCPA
in California also make Privacy Policies mandatory for many businesses dealing
with user information.
When and Why a Privacy Policy is Needed
A Privacy
Policy is required whenever a business or organisation collects personal
information from users. Even a simple website that asks users to fill in a
contact form with their name, email address, or phone number may require a Privacy
Policy. Similarly, websites using cookies, analytics tools, payment gateways,
newsletters, login systems, or online consultation features also need a proper
Privacy Policy. Businesses such as e-commerce companies, legal-tech platforms,
healthcare portals, educational websites, fintech applications, SaaS companies,
and online marketplaces commonly collect large amounts of user data and
therefore require comprehensive Privacy Policies. In fact, any organisation
handling customer information should ideally have a Privacy Policy to maintain
transparency and legal compliance.
The purpose
of a Privacy Policy is not limited to legal compliance alone. One of its
biggest purposes is to build trust among users. People are more likely to use a
service when they know their personal information is safe and protected. A
clear and transparent Privacy Policy gives users confidence that the platform
values their privacy and follows responsible data practices. This becomes even
more important for businesses dealing with confidential or sensitive
information such as legal services, healthcare consultations, financial
transactions, or identity verification.
Another
important purpose of a Privacy Policy is obtaining user consent. When users
access a platform or submit their information, the Privacy Policy informs them
about how their data will be used and shared. This creates informed consent
between the user and the company. For example, if a legal-tech platform shares
client information with advocates or professional consultants for service
delivery purposes, such sharing should be clearly disclosed in the Privacy
Policy. Similarly, if a website sends promotional emails, SMS alerts, or
WhatsApp messages, the Privacy Policy should mention this clearly so that users
are aware of such communications.
A
well-drafted Privacy Policy also protects businesses from future disputes and
legal complications. If a company clearly explains its data collection and
usage practices beforehand, users cannot later claim that they were unaware of
how their information was being handled. This reduces misunderstandings and
provides legal protection to the business in case of disputes regarding privacy
or misuse of data.
Essential Clauses of a Good Privacy Policy
A good
Privacy Policy generally contains several standard clauses which are considered
essential for transparency and compliance. One of the most important clauses is
the information collection clause. This section explains what types of
information the company collects from users. Such information may include
personal details like name, phone number, email address, date of birth,
address, payment details, uploaded documents, and identity verification
records. It may also include technical information such as IP address, browser
details, device information, cookies, location data, and browsing behaviour.
Another
essential clause is the purpose of data usage clause. This section explains why
the information is being collected and how it will be used. Businesses usually
collect data for providing services, customer support, payment processing,
account management, communication, analytics, fraud prevention, and improving
user experience. The Privacy Policy should clearly explain these purposes in
simple language so that users understand how their information contributes to
service delivery.
A strong
Privacy Policy also contains a data sharing clause. In modern businesses,
especially online platforms, user data is often shared with third-party service
providers such as payment gateways, cloud storage providers, technical support
vendors, consultants, or professional service providers. For example, a legal
platform may share user documents with advocates handling a case. A Privacy
Policy should clearly state with whom the information may be shared and for
what purpose. It should also mention that such third parties are bound by
confidentiality obligations and are permitted to use the data only for
authorised purposes.
The data
security clause is another crucial component of a good Privacy Policy. Users
want assurance that their information is protected from hacking, misuse, or
unauthorised access. Therefore, the policy should mention the security measures
adopted by the company such as encryption, firewalls, secure servers,
authentication systems, restricted access controls, and internal security
protocols. Although no online system can be completely secure, a Privacy Policy
should demonstrate that the company takes reasonable precautions to protect
user data.
A modern
Privacy Policy should also include a data breach notification clause. In case
user data is compromised due to a cyberattack, technical failure, or security
breach, users should be informed appropriately. Many modern privacy laws
encourage organisations to notify affected users within a reasonable time after
becoming aware of a breach. Including such a clause reflects transparency and
accountability.
Another
important clause is the cookies and tracking technologies clause. Many websites
use cookies and analytics tools to improve functionality and understand user
behaviour. A Privacy Policy should explain what cookies are, why they are used,
and whether users can disable them through browser settings.
The user
rights clause has also become increasingly important under modern data
protection laws. This section informs users about their rights regarding their
personal information. Such rights may include accessing their data, correcting
inaccurate information, requesting deletion, withdrawing consent, or
restricting certain processing activities. Providing these rights demonstrates
fairness and respect for user privacy.
For platforms
handling sensitive information such as legal consultations, healthcare records,
or financial details, confidentiality clauses are extremely important.
Legal-tech platforms, for example, should clarify that communications between
users and advocates remain privileged and confidential under applicable laws.
Even if limited access is provided to authorised staff for operational support,
such access should not amount to waiver of legal privilege.
Children’s
privacy is another important area addressed in Privacy Policies. Most platforms
specify that their services are intended only for users above 18 years of age
and that they do not knowingly collect information from minors without parental
or guardian consent. This helps businesses comply with laws relating to child
data protection.
In conclusion, a
Privacy Policy is no longer just a formality or optional legal document. It is
an essential part of every modern business that collects or handles user
information. It protects users by informing them about their privacy rights and
protects businesses by ensuring transparency and legal compliance. A good
Privacy Policy builds trust, improves credibility, prevents disputes, and
demonstrates that the company values privacy and responsible data handling
practices. In today’s digital environment where personal information has become
extremely valuable and sensitive, maintaining a clear, transparent, and
user-friendly Privacy Policy is not only a legal necessity but also a sign of
professionalism and ethical business conduct.
privacy policy, draft privacy policy, how to draft
privacy policy, privacy policy india, what is privacy policy, importance of
privacy policy, privacy policy for website, privacy policy for business,
privacy policy for startup, legal privacy policy, website privacy policy, data
protection policy, online privacy policy, privacy policy draft, privacy policy
clauses, privacy policy requirements, privacy policy under indian law, digital
personal data protection act, DPDP Act 2023, IT Act 2000, data privacy laws
india, user data protection, personal data protection, privacy law india, legal
compliance for websites, legal requirements for websites, website legal
documents, terms and privacy policy, privacy policy for legal tech platform,
privacy policy for ecommerce website, privacy policy for mobile apps, privacy
policy for online business, privacy policy template india, data security
policy, user consent policy, cookies policy, data collection policy, personal
information protection, GDPR and privacy policy, website compliance india,
cyber law india, legal drafting, legal article, legal awareness, online data
security, privacy rights, consumer data protection, advocate client
confidentiality, digital privacy, legalkonnect, legifolio llp, legal blog
india, legal website compliance, privacy policy for lawyers, privacy policy for
consultation platform, indian cyber laws, website privacy compliance, privacy
protection online, legal documentation, business compliance, privacy policy
explained, why privacy policy is important, mandatory privacy policy, standard
privacy policy clauses, website user privacy, internet privacy laws, online
legal services, confidentiality policy, legal content india, startup legal
compliance, legal knowledge, professional legal services, data sharing policy,
third party data sharing, privacy and security, privacy policy article,
humanized legal article, law and technology, digital law india, privacy policy
for companies, online platform compliance, legal information article, cyber
compliance, privacy regulations india, business law india